🔒 Your critical assets deserve better than just a firewall. And you deserve to be able to sleep soundly.
With the implementation of NIS2, one question keeps cropping up amongst CISOs and senior management at critical infrastructure organisations: “How can we set up data exchanges whilst ensuring that critical assets remain inaccessible, even in the event of a total network compromise?”
All other so-called ‘air gap’ solutions answer this question… by creating a flow between the networks. A restricted flow, a one-way flow, a temporary flow… but a flow nonetheless – a smaller door, but one that is very much open.
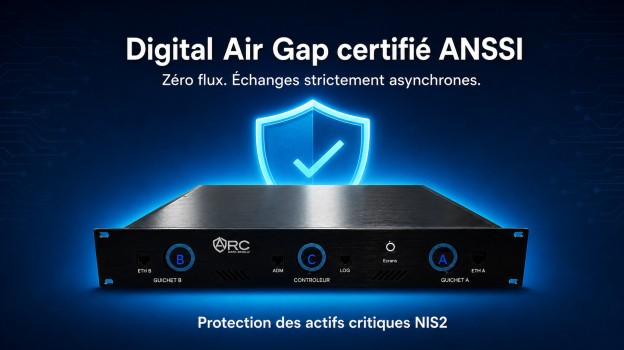
The Digital Air Gap goes a step further: no connection is ever established. Not even a partial, one-way or temporary one: NONE.
In practical terms, our architecture is based on a patented, strictly asynchronous exchange. There is simply never a moment when an active communication channel connects the protected asset to the exposed network.
Why this changes everything:
✅ No data flow = no attack surface, however small
✅ No exploitable protocols, no paths an attacker can hijack, no lateral movement possible
✅ Ransomware, even in the event of a complete compromise of the upstream infrastructure, cannot reach or corrupt the isolated
asset ✅ Constant, verifiable isolation that does not depend on any window of human or technical vigilance.
How does this differ from other ‘air gap’ solutions? They reduce or minimise the duration of exposure. We, on the other hand, eliminate it altogether.
It is this approach that has enabled our solution to achieve ANSSI certification, confirming its compliance with the most stringent requirements for the protection of critical assets under NIS2.
At Arc Data Shield, we protect what cannot be exposed — not even for a second.